Binance Attack Spurs Risk Management Debate Around Vietnam’s Crypto Asset Pilot
Cybersecurity expert Ngô Minh Hiếu says the Binance attack exposed risks in transaction permissions, asset custody and incident response. As Vietnam conducts a five-year crypto asset market pilot, he calls for independent verification, clearer incident reporting and stronger investor protection.

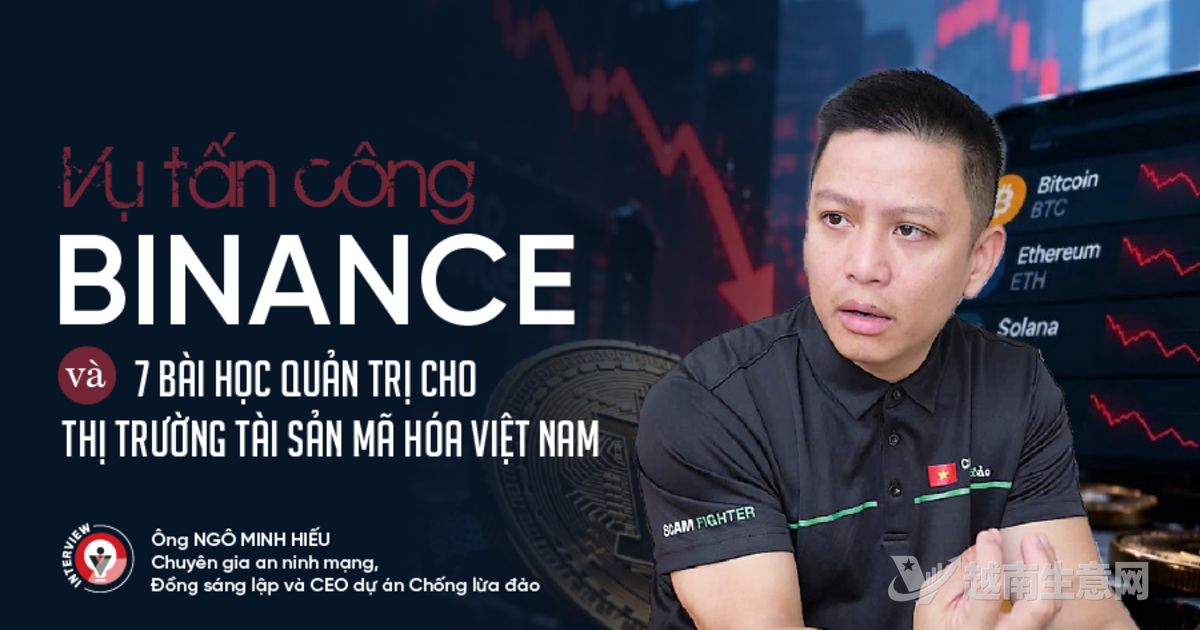
Cybersecurity expert Ngô Minh Hiếu said Binance was attacked on October 29, 2026. According to Binance’s November 3 update, crypto assets worth an estimated $6.34 billion were transferred without authorization. About $2.85 billion in assets had been frozen or blocked through cooperation with partners. He stressed that freezing assets does not mean they have been recovered and returned to users.
He said the incident highlighted risks involving privileged personnel and devices, transaction approval and signing processes, interconnected system permissions, and third-party services. Binance’s preliminary report described a multistage intrusion involving multiple devices and internal systems. The investigation is ongoing; no evidence of a private key leak has been found, but that finding alone does not establish the cause of the incident. Platforms should introduce automatic pauses for unusual transactions and limit the losses any single account could cause.
Binance has announced that it will compensate users for their losses, but company compensation is separate from recovering stolen assets. Ngô Minh Hiếu said tracing, blocking, freezing and returning assets requires cooperation among platforms, asset issuers and relevant authorities. The conditions for freezing assets also vary by asset, and full recovery cannot be guaranteed.
Vietnam’s Resolution No. 05/2025/NQ-CP took effect on September 9, 2025, establishing a five-year crypto asset market pilot. Ngô Minh Hiếu recommended verifying that customer assets are kept separate from company assets, conducting independent security assessments and incident response drills, building domestic tracing and emergency response capacity, and setting out detailed procedures for incident reporting and coordination. The resolution requires unusual-event disclosures within 24 hours for information technology incidents that affect customers’ crypto asset transactions. He also recommended adjusting regulatory requirements to market size and product complexity and improving investor education.
Source: VietVance