Vietnamese SMEs Face Data Security and Compliance Challenges in International Markets
At a November 17 seminar, the Vietnam Chamber of Commerce and Industry warned that SMEs expanding internationally must manage cyberattacks, internal data practices and legal compliance. Experts advised businesses to assign responsibility for data processing, restrict access and complete required filings.

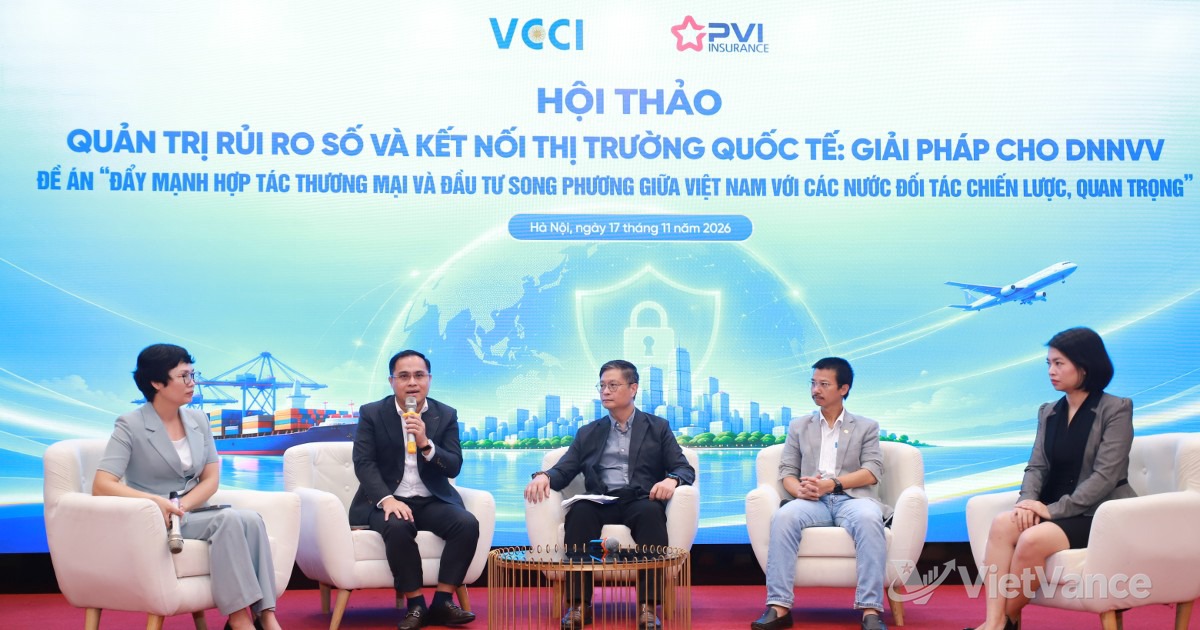
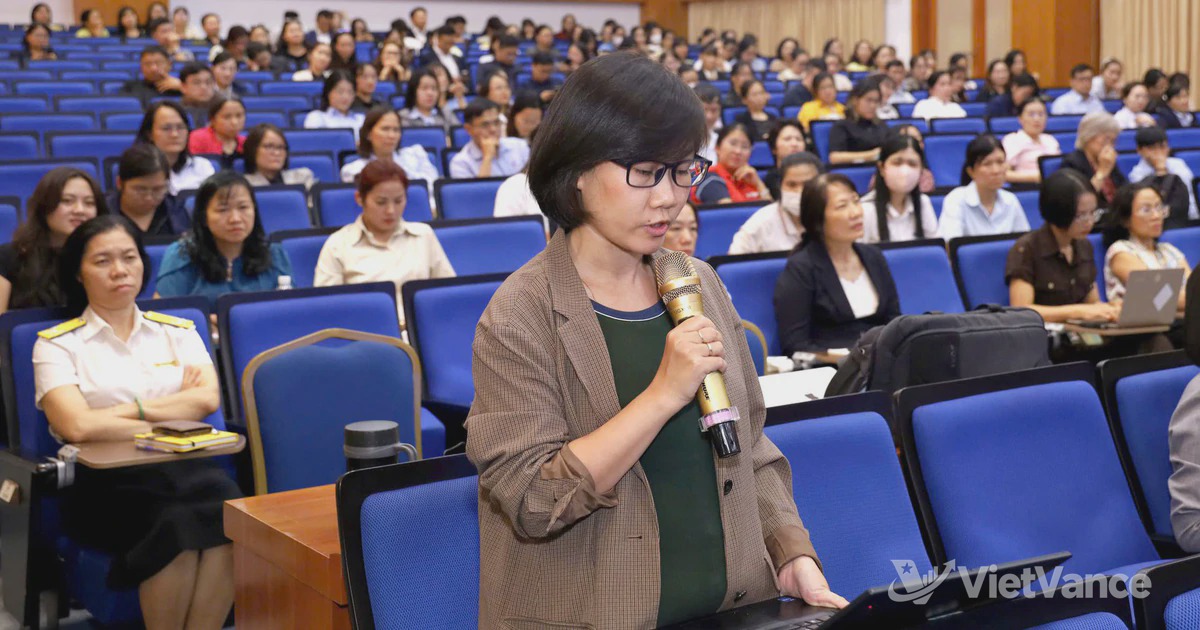
The Vietnam Chamber of Commerce and Industry and PVI Insurance Corporation held a seminar on November 17, 2026, to discuss digital risk management and access to international markets for small and medium enterprises (SMEs). Trần Thị Thanh Tâm, head of the chamber’s SME support center, said digital platforms help small businesses reach customers across borders but also expose customer data, operating systems and commercial reputations to greater risk.
According to Vietnam’s National Business Registration Database, small, medium and micro enterprises accounted for about 98% of the country’s more than 1 million active businesses as of December 31, 2025. Figures from the National Cybersecurity Association show that Vietnam recorded about 552,000 cyberattacks in 2025; 52.3% of surveyed businesses suffered losses, and information from about 25.5 million accounts was leaked.
Data security risks also arise from companies’ internal management. Cybersecurity expert Ngô Việt Khôi said some SMEs lack dedicated staff, use the same accounts for personal and work purposes, store customer data across multiple locations, and leave access permissions in place after employees depart. These weaknesses can affect business operations and transactions.
Lawyer Lưu Xuân Vĩnh noted that the Personal Data Protection Law, which took effect on January 1, 2026, requires businesses to complete documentation and submit it to the Ministry of Public Security’s cybersecurity department within 60 days of beginning to process personal data. Businesses must also pay attention to Cybersecurity Law No. 116/2025/QH15, which took effect on July 1, 2026, and its accompanying regulations, and clarify where their data comes from, where it is stored and the legal basis for processing it.
Nguyễn Tiến Đức, an official with the Ministry of Public Security’s cybersecurity department, advised businesses to review their information systems, determine their security levels and appoint a person responsible for cybersecurity. Experts at the seminar also recommended restricting access to customer and financial data and carefully reviewing data processing practices when using customer relationship management software or artificial intelligence tools hosted on overseas servers. Trần Thị Thanh Tâm said businesses seeking to enter international supply chains must also demonstrate that they can maintain stable operations and protect customer data.
Source: VietVance