Vietnam Passes Data Security Law With Five Risk Levels
Vietnam’s National Assembly passed the Data Security Law on November 20. Effective July 1, 2027, it classifies data security risks into five levels and sets protection requirements for data controllers, foreign organizations, third-party processors and AI training data.

Vietnam’s National Assembly passed the Data Security Law on November 20 with 468 votes in favor. The law will take effect on July 1, 2027. Its six chapters and 28 articles set out data security measures and the rights and responsibilities of agencies, organizations and individuals.
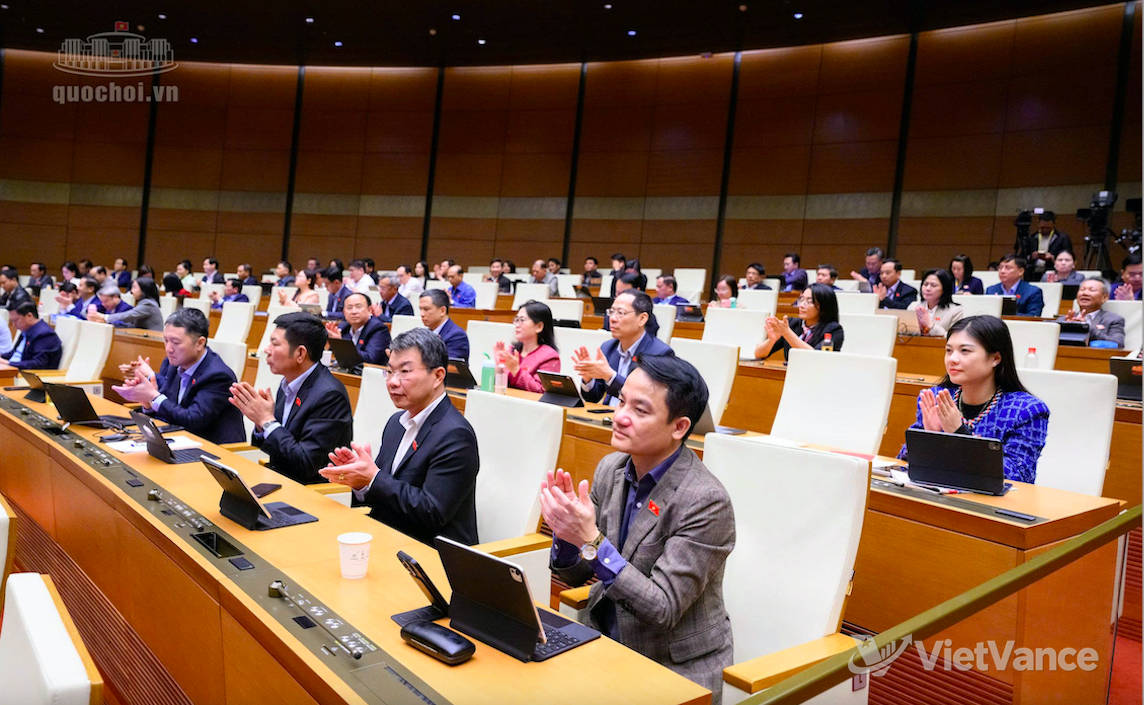
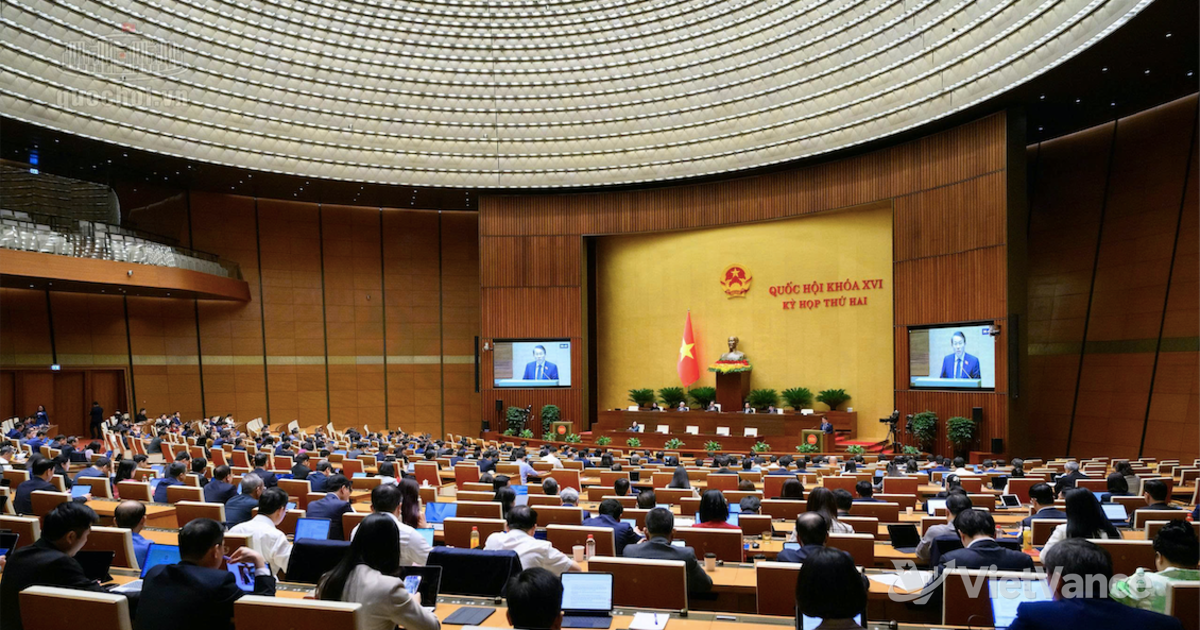
Vietnam’s National Assembly votes to pass the Data Security Law.(VietVance)
The law applies to organizations and individuals in Vietnam, as well as those outside the country that process data under Vietnam’s jurisdiction or compromise Vietnam’s data security. Data security protections must begin at the system design stage and continue through data creation, collection, storage, processing, transmission, sharing and deletion.
The law classifies data security risks into five levels according to the potential harm. Data controllers must assess risk levels themselves and take corresponding measures. For Level 1 and Level 2 data, controllers are primarily responsible for their own protections. Level 3 data and above face stricter risk impact assessment and security audit requirements. Level 4 and Level 5 data must be audited, with the results submitted to the competent authority.
Telecommunications, internet, data center and cloud computing service providers must protect data security within the scope of their technical control over services and the responsibilities agreed with customers. Data controllers remain responsible for their obligations even when they engage third parties to process data. Processors must handle data within the agreed scope and for the agreed purposes, and hand over or destroy all data when the contract ends, unless the law provides otherwise.
The law also sets requirements for AI training data, including identifying and removing fabricated, distorted or malware-containing data. Using Level 3 or higher data from the defense and security sectors to train AI models requires approval from the competent authority. The law prohibits deliberately understating data risk levels, concealing data security incidents, and illegally trading or disclosing data, among other acts.
Source: VietVance